Fix Joomla 3 Security Issues in One Click
Joomla 3 is end of life. The official project stopped releasing public updates at 3.10.12, but new vulnerabilities keep turning up. There used to be a paid safety net: Joomla’s Extended Long Term Support programme backported fixes to Joomla 3 for a subscription, but it ended on 17 February 2025 and has shipped nothing since. Every Joomla core release since then has fixed issues that reach Joomla 3, with no official patch for them on Joomla 3 at all. Joomla’s September 2026 release, 5.4.9, fixed sixteen more core issues, and most reach back through the whole 3.x series. We backported every one that applies, and while checking it we found five from the spring that had slipped past us too. The tool went from 65 files to 85.
Manually patching 85 files per site is tedious enough when you have five sites. When you have five hundred, forget it.
mySites.guru fixes every known Joomla 3 security issue with a single click.
We include all Joomla 3 security fixes in the service. No eLTS subscription needed.
How Does It Work?
The patch tool is in the Site Snapshot for each Joomla 3.10.12 site in your mySites.guru account. One toggle. That’s it.
Note: the toggle works on any Joomla 3.10.12 install. The tool ships every patch through to the final eLTS backport (3.10.20-elts, the last one before the programme closed) and every core fix disclosed since, so flipping it on brings the site right up to date in one go.
Under the hood, the mySites.guru connector tracks the MD5 hash of each file that needs patching. Flip the toggle on and it compares hashes against the expected patched versions, replacing anything that doesn’t match. Flip it off and the files revert to stock 3.10.12.
The tool only runs on Joomla 3.10.12, the last publicly released version of the Joomla 3 series. It ignores the commercial eLTS programme entirely.
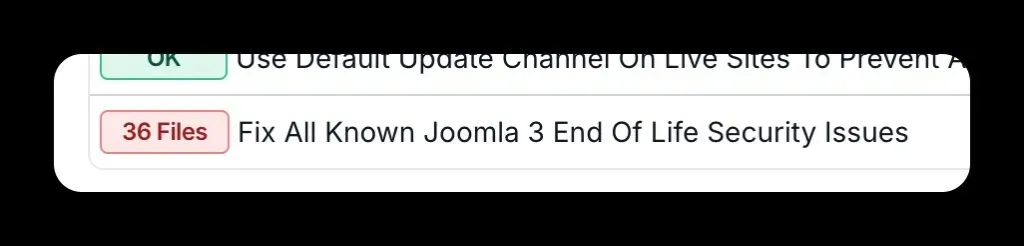
Where Do You Find the Tool?
Two ways to get there:
- Cmd+K and search for “Fix All Known Joomla 3”
- Open your site’s Snapshot and scroll to the Joomla Configuration section
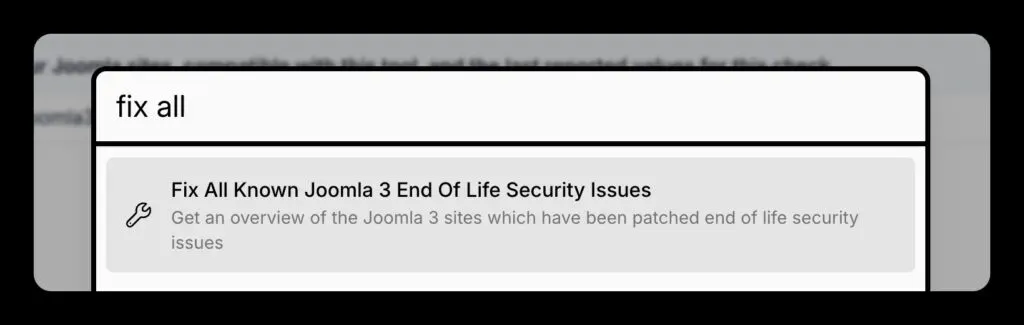
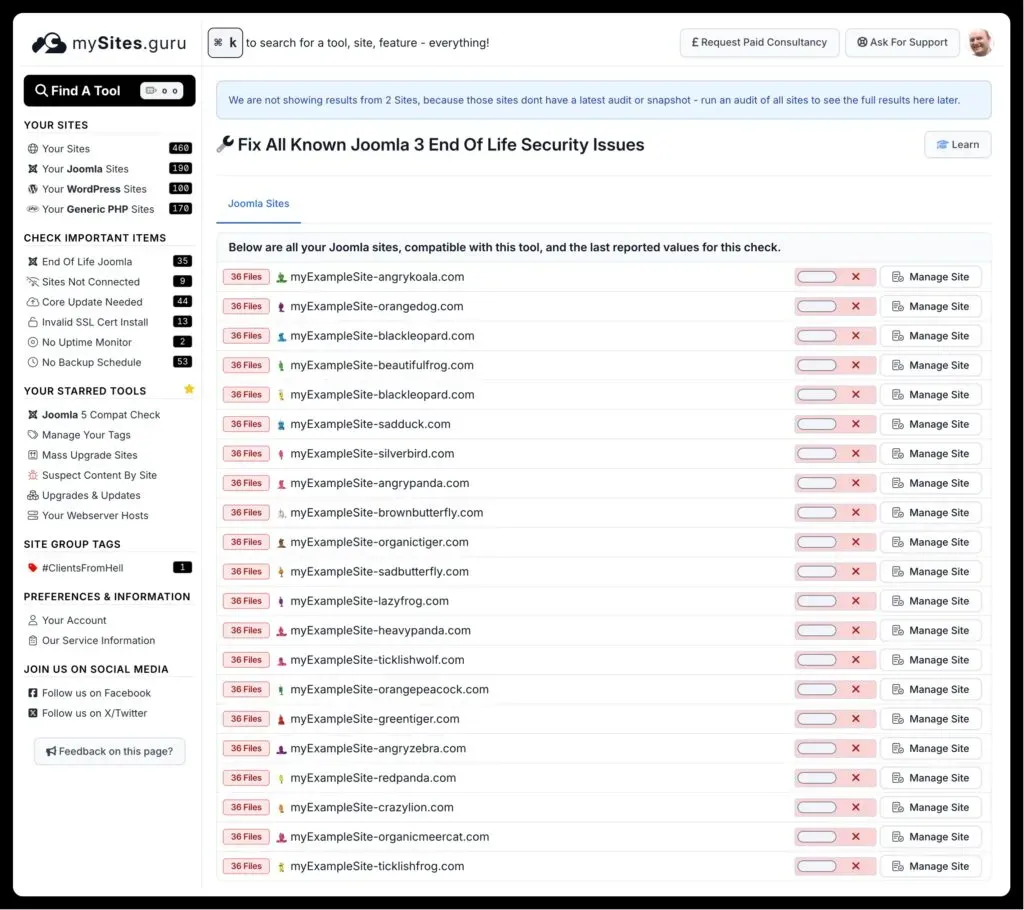
Both paths lead to a tool overview page listing every Joomla 3.10.12 site you manage, along with each site’s current patch status.
How Do You Patch Multiple Sites at Once?
Got dozens or hundreds of Joomla 3 sites? Click the grid icon next to the toggle to open the bulk view. It shows every Joomla 3.10.12 site with individual toggles. If you’re managing multiple Joomla sites from a single dashboard, this bulk view is where you’ll spend most of your time.

Direct link: manage.mysites.guru/en/tools/allsites/Joomla/joomlaconfiguration/joomla3eol
What vulnerabilities does it fix?
Individually, most of these will not get your site hacked while you sleep. But stacked together across an unpatched site, they add up, and a few (the SHTML upload, the SSRF, the cache directory-deletion) are serious on their own. The patch covers 85 files and addresses every known vulnerability disclosed since 3.10.12:
XSS vulnerabilities
- CVE-2024-21724 - XSS in media selection fields
- CVE-2024-21725 - XSS in mail address outputs
- CVE-2024-21726 - Inadequate content filtering within the filter code
- CVE-2024-21731 - XSS in StringHelper::truncate method
- CVE-2024-26278 - XSS in com_fields default field value
- CVE-2024-26279 - XSS in Wrapper extensions
- CVE-2024-40743 - XSS vectors in Outputfilter::strip* methods
- CVE-2024-40747 - XSS vectors in module chromes
- CVE-2024-40748 - XSS vector in the id attribute of menu lists
- CVE-2025-63083 - XSS vector in the pagebreak plugin
- CVE-2026-48954 - XSS through language overrides
- CVE-2025-54476 - Inadequate content filtering in the checkAttribute filter code
- CVE-2025-63082 - Inadequate content filtering for data URLs (Joomla says 4.0+, the code is also in 3.10.12)
- CVE-2026-25900 - XSS in feed modules
- CVE-2026-30894 - XSS in com_contenthistory
- CVE-2026-48903 - Inadequate content filtering in the checkAttribute filter code
- CVE-2026-48905 - Inadequate content filtering in the cleanAttributes filter code
- CVE-2026-90906 - XSS in the HTMLHelper::link method
- CVE-2026-92225 - XSS in the module list (Joomla says 4.0+, the code is also in 3.10.12)
- CVE-2026-92231 - XSS filter bypass in InputFilter via HTML5 entity decode mismatch
- CVE-2026-92232 - XSS filter bypass in InputFilter via whitespace in HTML data URIs
Other vulnerabilities
- CVE-2024-27184 - Inadequate validation of internal URLs
- CVE-2024-27185 - Cache poisoning in pagination
- CVE-2024-21723 - Open redirect in installation application
- CVE-2024-21722 - Insufficient session expiration in MFA management views
- CVE-2023-40626 - Exposure of environment variables
- CVE-2024-40749 - Read ACL violation in multiple core views
- CVE-2025-22213 - Malicious file uploads via Media Manager
- CVE-2025-25226 - SQL injection in the quoteNameStr method of the database package
- CVE-2026-48948 - Incorrect access control in the com_contact vCard download
- CVE-2026-71572 - Response header injection in download views
- CVE-2026-73373 - Unrestricted uploads of SHTML files
- CVE-2026-48902 - Transport encryption downgrade for password and username reset links
- CVE-2026-40383 - Local file inclusion in the HtmlView layout parameter
- CVE-2026-90907 - Unauthorized user account creation via the profile.save controller
- CVE-2026-92222 - SSRF vectors in various core extensions
- CVE-2026-90915 - Arbitrary directory deletion via the cache purge action (Joomla says 4.0+, the code is also in 3.10.12)
- CVE-2026-90916 - Improper ACL checks in the content history comparison view (Joomla says 4.0+, the code is also in 3.10.12)
- CVE-2026-90917 - Improper ACL checks in outputs for tagged items (Joomla says 4.0+, the code is also in 3.10.12)
eLTS bug-fix-for-bug-fix patches
- Fixes in 3.10.19-elts that repair broken code shipped in 3.10.18-elts
- Fixes in 3.10.18-elts that repair broken code shipped in 3.10.17-elts
How Do Patched Files Show Up in Audits?
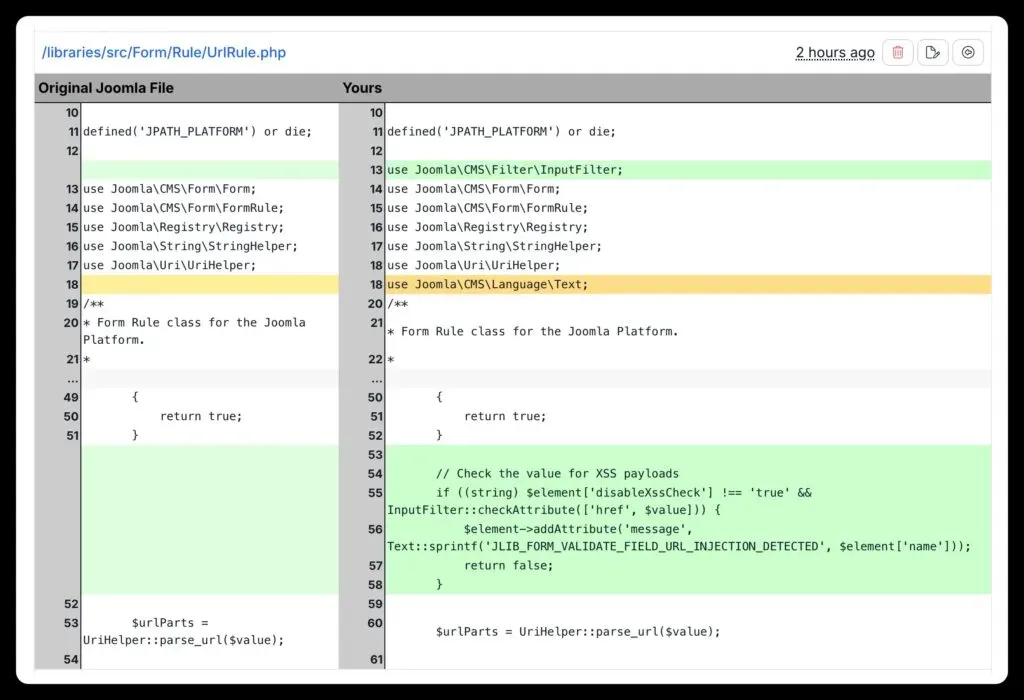
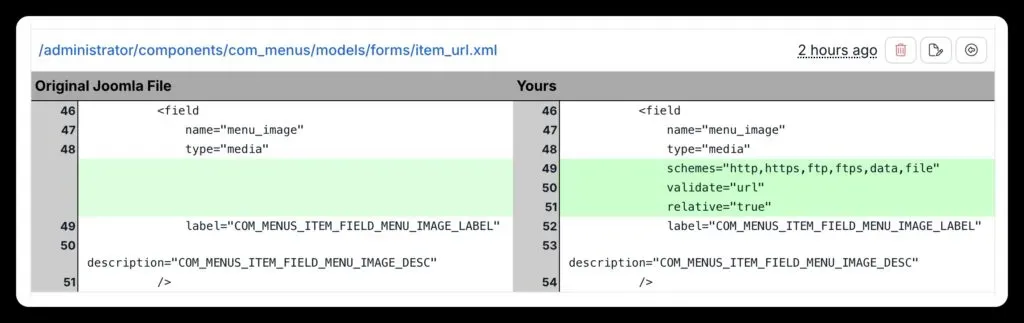
After patching, your mySites.guru audit will flag the modified files as Core File Changes, because they are changes to the original 3.10.12 distribution. You can inspect every diff directly in the audit tool.
Which Files Does the Patch Modify?
The tool touches 85 files: 43 PHP files (the actual security fixes), 37 XML form definitions (tighter input validation), three language files and two CA certificate bundles. You need all of them. Changing the XML alone isn’t enough.
Eighty-four of those are replaced with patched versions. One is a file Joomla 3 never shipped at all: the form rule behind the language override fix. Toggling on creates it, and toggling off deletes it again.
Full list of patched files (85 files)
- administrator/components/com_banners/models/forms/banner.xml
- administrator/components/com_categories/models/forms/category.xml
- administrator/components/com_config/model/form/application.xml
- administrator/components/com_contact/config.xml
- administrator/components/com_contact/models/forms/contact.xml
- administrator/components/com_content/models/forms/article.xml
- administrator/components/com_contenthistory/models/compare.php
- administrator/components/com_contenthistory/views/preview/tmpl/preview.php
- administrator/components/com_fields/models/forms/field.xml
- administrator/components/com_joomlaupdate/config.xml
- administrator/components/com_languages/models/forms/override.xml
- administrator/components/com_languages/models/rules/disallowquotes.php (added, not replaced)
- administrator/components/com_media/controllers/file.php
- administrator/components/com_menus/models/forms/item_alias.xml
- administrator/components/com_menus/models/forms/item_component.xml
- administrator/components/com_menus/models/forms/item_heading.xml
- administrator/components/com_menus/models/forms/item_separator.xml
- administrator/components/com_menus/models/forms/item_url.xml
- administrator/components/com_menus/models/forms/itemadmin_alias.xml
- administrator/components/com_menus/models/forms/itemadmin_component.xml
- administrator/components/com_menus/models/forms/itemadmin_container.xml
- administrator/components/com_menus/models/forms/itemadmin_heading.xml
- administrator/components/com_menus/models/forms/itemadmin_url.xml
- administrator/components/com_modules/views/modules/tmpl/default.php
- administrator/components/com_newsfeeds/models/forms/newsfeed.xml
- administrator/components/com_tags/models/forms/tag.xml
- administrator/components/com_users/models/user.php
- administrator/language/en-GB/en-GB.com_config.ini
- administrator/language/en-GB/en-GB.com_languages.ini
- administrator/language/en-GB/en-GB.lib_joomla.ini
- administrator/modules/mod_feed/mod_feed.xml
- administrator/modules/mod_feed/tmpl/default.php
- administrator/templates/hathor/templateDetails.xml
- administrator/templates/isis/templateDetails.xml
- components/com_contact/views/contact/view.vcf.php
- components/com_content/models/forms/article.xml
- components/com_content/views/archive/view.html.php
- components/com_finder/views/search/view.html.php
- components/com_privacy/controller.php
- components/com_privacy/privacy.php
- components/com_search/views/search/view.html.php
- components/com_tags/views/tag/tmpl/default.xml
- components/com_tags/views/tag/tmpl/list.xml
- components/com_tags/views/tags/tmpl/default.xml
- components/com_users/controller.php
- components/com_users/controllers/profile.php
- components/com_users/models/profile.php
- components/com_users/models/remind.php
- components/com_users/models/reset.php
- components/com_users/users.php
- components/com_users/views/login/tmpl/default.xml
- components/com_wrapper/views/wrapper/tmpl/default.xml
- includes/framework.php
- libraries/cms/html/string.php
- libraries/fof/download/adapter/cacert.pem
- libraries/joomla/database/driver.php
- libraries/src/Cache/Cache.php
- libraries/src/Cache/Storage/FileStorage.php
- libraries/src/Feed/Parser/RssParser.php
- libraries/src/Filter/InputFilter.php
- libraries/src/Form/Rule/UrlRule.php
- libraries/src/Helper/MediaHelper.php
- libraries/src/Helper/ModuleHelper.php
- libraries/src/Helper/TagsHelper.php
- libraries/src/HTML/HTMLHelper.php
- libraries/src/Http/Transport/cacert.pem
- libraries/src/Language/LanguageHelper.php
- libraries/src/MVC/View/HtmlView.php
- libraries/src/Pagination/Pagination.php
- libraries/src/Uri/Uri.php
- libraries/vendor/joomla/filter/src/InputFilter.php
- libraries/vendor/joomla/filter/src/OutputFilter.php
- modules/mod_custom/mod_custom.xml
- modules/mod_feed/mod_feed.xml
- modules/mod_feed/tmpl/default.php
- modules/mod_menu/tmpl/default.php
- modules/mod_tags_popular/helper.php
- modules/mod_tags_similar/helper.php
- modules/mod_wrapper/mod_wrapper.xml
- plugins/content/pagebreak/pagebreak.php
- plugins/system/sef/sef.xml
- plugins/user/profile/profile.php
- plugins/user/profile/profiles/profile.xml
- templates/beez3/templateDetails.xml
- templates/protostar/templateDetails.xml
Why Does Joomla 3 Still Matter?
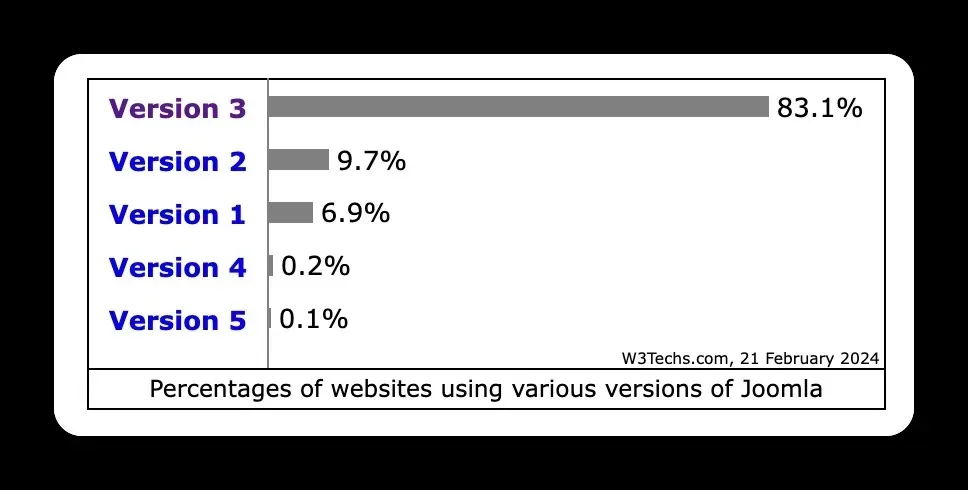
Joomla 3 is still everywhere. W3Techs shows version 3 running on the majority of Joomla installations, and Joomla’s own usage statistics put 3.10.x at over 35% of reporting sites.
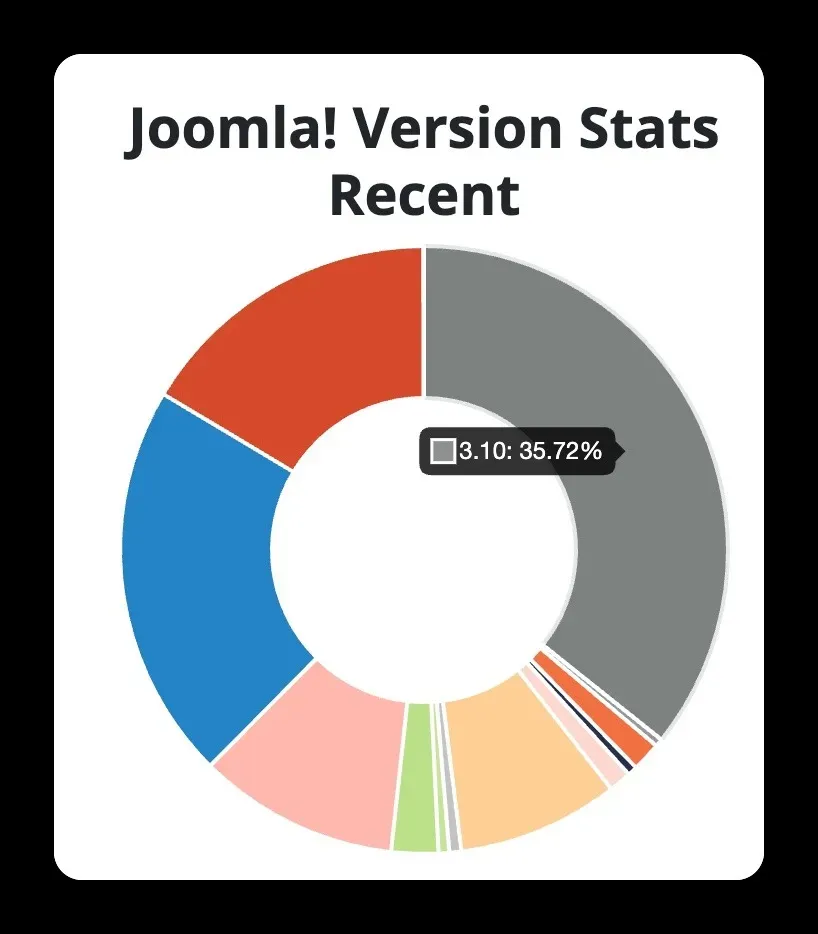
If you run a digital agency, you already know: migrating clients from Joomla 3 to 4 or 5 takes budget, developer time, and client sign-off. That doesn’t happen overnight, and the sites still need protecting in the meantime.
What Is the Joomla 3.10.999 Project?
The patches in mySites.guru come from the open-source Joomla 3.10.999 project. That repo has every Joomla 3.10 version from 3.10.12 onwards, plus diffs for all patches released under the commercial eLTS programme.
Same approach as the earlier Joomla 1.5.999 and Joomla 2.5.999 repos. It’ll be maintained for as long as Joomla 3 sites exist.
Stop patching files by hand
If you’re still running Joomla 3, stop tracking CVEs by hand. Add your sites to mySites.guru, flip the toggle, and get on with your day.
The broader picture of securing Joomla and WordPress sites is covered in the WordPress and Joomla security guide. For Joomla-specific agency workflows, see the Joomla agency handbook.
Frequently Asked Questions
Can I fix Joomla 3 security vulnerabilities without manually editing files?
How many files does the mySites.guru Joomla 3 patch tool modify?
What types of security issues does the Joomla 3 patch tool fix?
Do I need a Joomla eLTS subscription to get these patches?
 Written and edited by a human, with AI assistance. Our approach to AI