YOOtheme Pro 5: A Critical Security Update Is Coming on 21 October
Update, 21 October 2026: YOOtheme Pro 5.0.53 is out
YOOtheme has released 5.0.53, the fix for CVE-2026-102785, an unauthenticated remote code execution via the image handler. Every YOOtheme Pro 5 build before it is affected. Update every Pro 5 site now and read the full write-up.
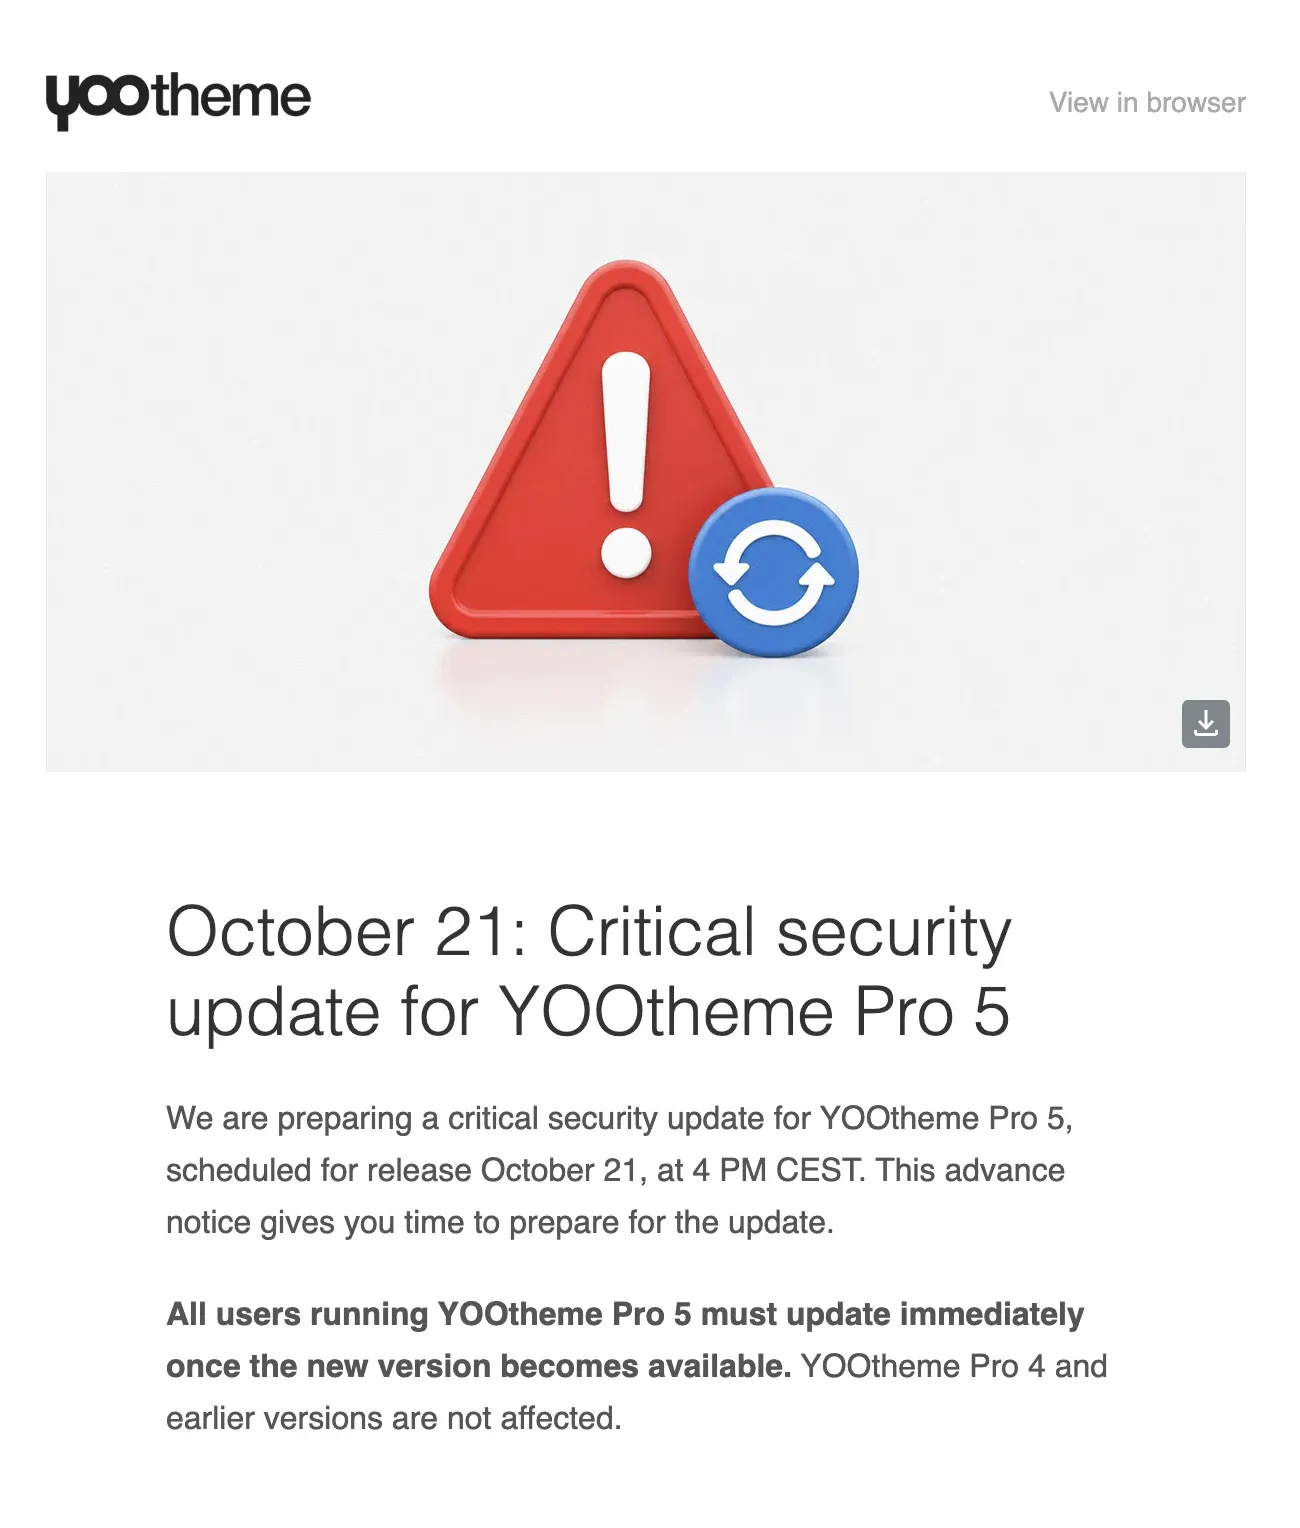
YOOtheme has given its customers advance notice of a critical security update for YOOtheme Pro 5, the Joomla page-builder template. The patched build is due on Wednesday 21 October 2026 at 16:00 CEST (14:00 UTC) and will appear in the YOOtheme Pro changelog. Every site running YOOtheme Pro 5 should update the moment it is out. YOOtheme Pro 4 and earlier are not affected.
Here is the vendor’s own notice, sent to customers on 20 October 2026: “We are preparing a critical security update for YOOtheme Pro 5, scheduled for release October 21, at 4 PM CEST. This advance notice gives you time to prepare for the update. All users running YOOtheme Pro 5 must update immediately once the new version becomes available. YOOtheme Pro 4 and earlier versions are not affected.” A day of advance notice is unusual for a Joomla extension vendor, and it is the right call: it gives anyone looking after a portfolio of client sites the evening to take backups and line up the sites that will need the update.
What we know so far
Very little, on purpose. We did not find this flaw and we have not investigated it; it was reported to YOOtheme by a third party, and the fix is not out yet. Publishing a guess at an unpatched critical issue only helps the people you do not want to help, so we are not going to describe something we have not seen fixed.
All the vendor has stated is that the issue is rated critical, that it affects every YOOtheme Pro 5 build, that YOOtheme Pro 4 and earlier are not affected, and that the fix is due on 21 October at 16:00 CEST. Once the release is out we will publish a full write-up here with the fixed version number and, if one is assigned, the CVE.
Only YOOtheme Pro 5 is affected
YOOtheme has been specific that this is a Pro 5 issue and that Pro 4 and earlier are not affected. Pro 5 runs on modern Joomla and is a separate codebase from the Pro 4 line, so the first job tonight is a version check. A site still on YOOtheme Pro 4 has nothing to do here, and time spent updating it tomorrow is time taken from the Pro 5 sites that need you.
mySites.guru already flags YOOtheme Pro 5
If your Joomla sites are connected to mySites.guru, the version check is done for you. A detection rule added on 20 October 2026 flags any connected site running YOOtheme Pro 5, so your next site snapshot lists exactly which sites need the update when the fix is out. YOOtheme Pro appears in the Joomla Vulnerability Database alongside the other extensions we track, and the alert clears when a later snapshot sees the patched version.
The rule went in a day before the patch exists. Most vulnerability alerts arrive after the fix, when the job is “update this”. This one arrives before, when the job is “know which sites to update at 16:00 CEST tomorrow”. If you manage more than a handful of Joomla sites, that list is the value of the alert; see managing multiple Joomla sites for how the rest of the workflow fits together. A free site audit shows the same finding on a site you have not connected yet.
What to do before the release
There is nothing that pre-empts this fix, so tonight is about preparation: a clean backup and a known list of the sites that will need the update.
- Confirm which sites run YOOtheme Pro 5. Pro 4 and earlier need no action.
- Take a fresh backup of every Pro 5 site before the release, so you can restore cleanly if an update goes wrong.
- Line up the affected sites in one list so you can move quickly tomorrow. mySites.guru builds this for connected sites.
- Update every YOOtheme Pro 5 site as soon as the build appears in the changelog at 16:00 CEST on 21 October 2026.
- Re-snapshot each site in mySites.guru afterwards so the alert clears.
We will publish the full write-up here once the release is out on 21 October.
Timeline
YOOtheme gives advance notice of a critical YOOtheme Pro 5 security update
The vendor tells customers that all YOOtheme Pro 5 sites must update as soon as the new version is available, and that YOOtheme Pro 4 and earlier are not affected. mySites.guru adds a detection rule for YOOtheme Pro 5 the same day.
Patched YOOtheme Pro 5 release due at 16:00 CEST (14:00 UTC)
Update every YOOtheme Pro 5 site as soon as the release appears in the changelog. A full write-up will follow here once it is out.
Further Reading
- YOOtheme Pro changelog - where the 21 October 2026 release and its version number will appear
- YOOtheme Pro in the mySites.guru Joomla Vulnerability Database - the entry that drives the detection rule on connected sites
- Treat an available Joomla extension update as a security flag - why an extension update you have not applied is a security finding, not a chore
Frequently Asked Questions
Is my site affected by the YOOtheme Pro 5 security update?
When is the YOOtheme Pro 5 fix available?
What are the details of the YOOtheme Pro 5 flaw?
Does mySites.guru detect the YOOtheme Pro 5 vulnerability?
What should I do before the patch is released?
 Written and edited by a human, with AI assistance. Our approach to AI